NorthSight Technologies is a Canadian software development firm in Ontario. We build custom software, review and secure code, and build production AI systems, under Canadian data residency and Protected-B / AODA standards. The Canada office of an allied practice with SmartOps in the UAE, with 28+ years of combined engineering.
We build custom software for Canadian organizations, review and secure the code, and help it stand up to the security and privacy reviews your buyers run.
Native and cross-platform apps, customer and staff portals, CRMs, dashboards, invoicing and HR systems, and the integrations that connect them. We ship the whole product, not just a prototype.
Custom software development →Software for buyers who run a security or privacy review before they sign. We build the access control, audit logs and Canadian data residency that SOC 2, HECVAT, PIPEDA and PHIPA questions ask about.
Software development with compliance experience →Independent secure code review and application-security remediation for Canadian SaaS vendors — and the help to pass the reviews that gate your deals: HECVAT, SOC 2, PIPEDA/PHIPA. We fix the code behind the answers, not just the paperwork.
Secure code review & app security →We also build AI, and the custom software around it, that public agencies and enterprises can put into production: accountable, secure and measured.
Multi-agent orchestration with structured outputs, validation gates and guardrails — taking pipelines from plausible drafts to a ~90% successful-run rate.
How we engineer agentic reliability →Retrieval systems that return grounded, citable answers — not confident hallucinations — backed by a golden-task eval set built from your real questions, so quality is measured.
Our eval-driven RAG approach →Turn slow, manual, repetitive processes into reliable AI workflows wired into the systems you already run — hours given back, with a clear audit trail.
What we automate & how →Wire LLMs into your platform and backend — Python, APIs, AWS/Azure — engineered for production, security and cost from day one.
Delivery aligned to Canadian Protected-B / AODA standards with data residency — plus privacy (PIPEDA, PHIPA), security assurance (SOC 2, ISO 27001) and health (HIPAA) frameworks — for when your AI touches sensitive or regulated data.
AI for government in Canada →Most AI doesn't fail because the model is weak — it fails because nobody engineered for the cases where it breaks. Our method takes AI from a convincing demo to something an organization can depend on and stand behind. Senior, accountable, and measurable.
We start where it's costing you — a focused look at where your AI, workflow or system breaks today, and what "good enough to ship" actually means for your organization.
Structured outputs, guardrails, retrieval and clean integration into your stack — engineered for production, security and compliance, not just a demo.
An evaluation harness so every improvement is provable, plus documentation and a clean handover so your team can own, audit and extend it.
Recent client work is largely proprietary, so these are genericized case studies — happy to walk through the real architecture and trade-offs on a call.
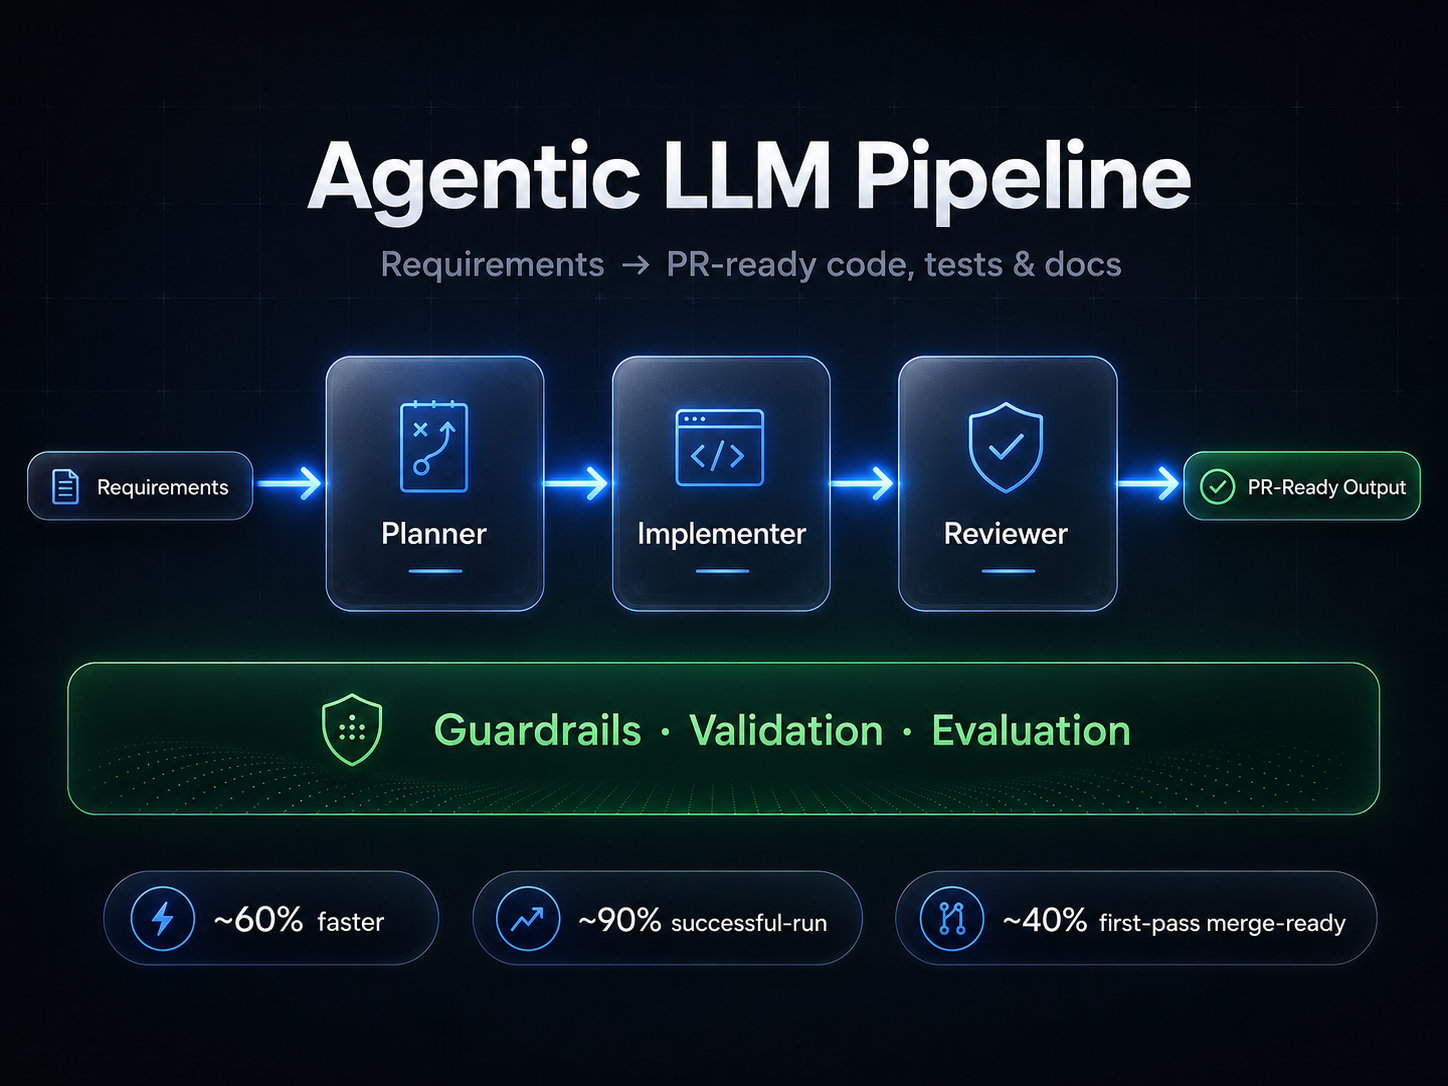
We designed a planner → implementer → reviewer pipeline that turns requirements into production-grade code, tests & docs — with structured outputs, validation gates, a failure taxonomy and an evaluation harness so quality is measured, not guessed.
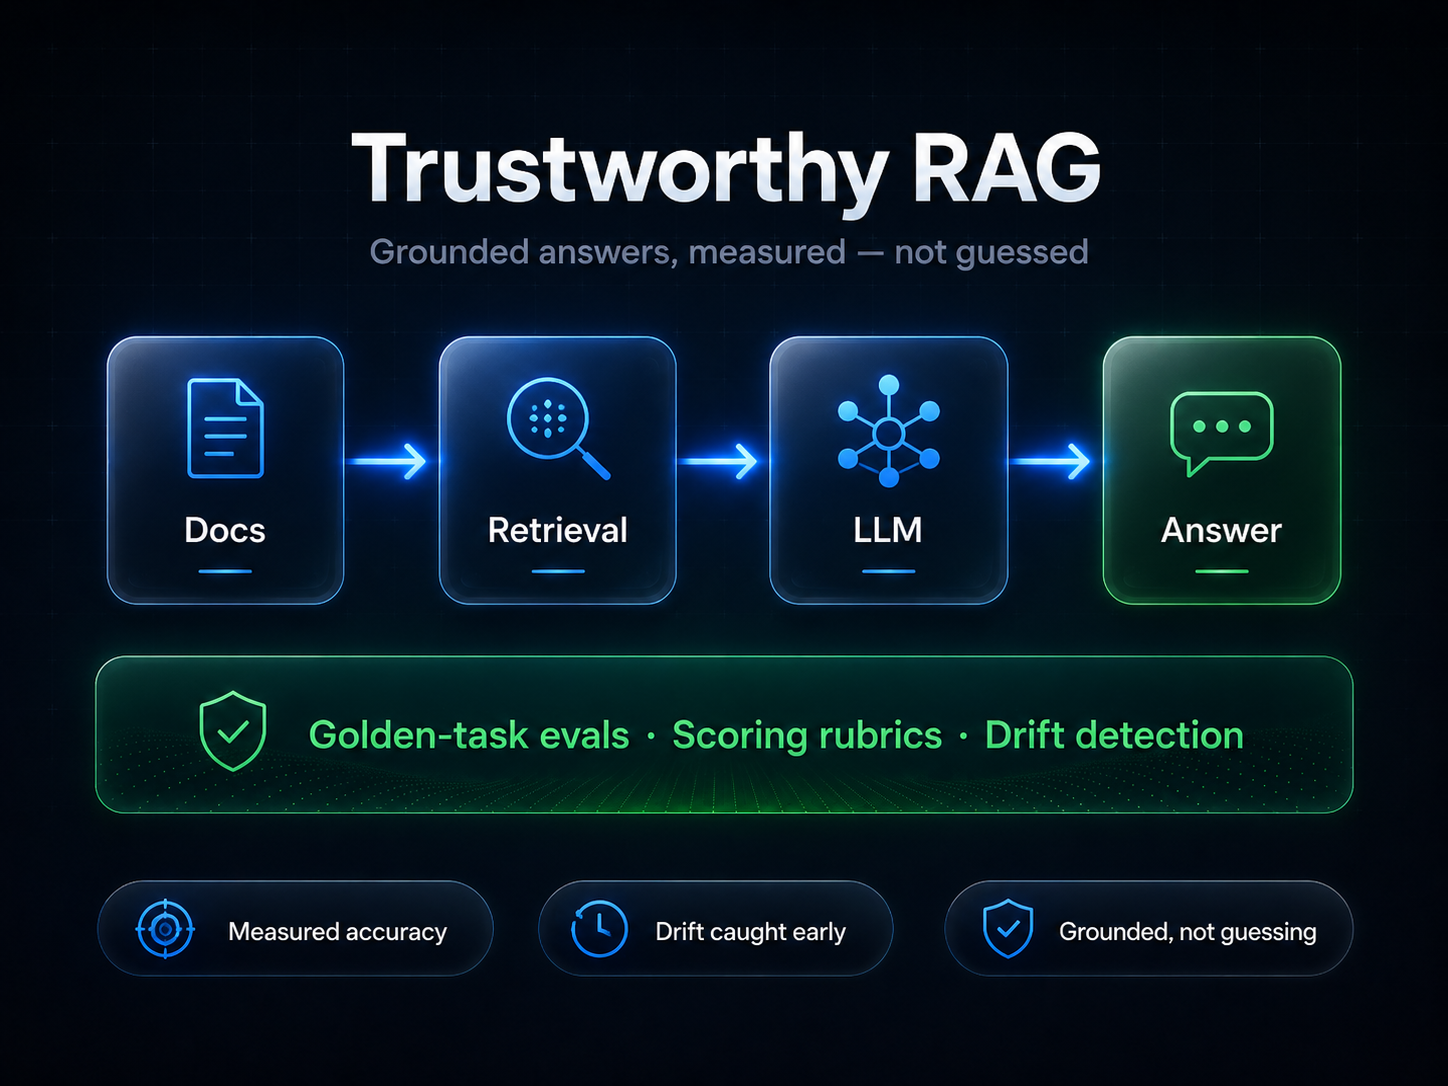
We treat RAG quality as an evaluation problem: ground answers in retrieval, then build a golden-task eval set from real user questions plus scoring rubrics and regression checks — so every change is measured against your data, and drift is caught before users see it.
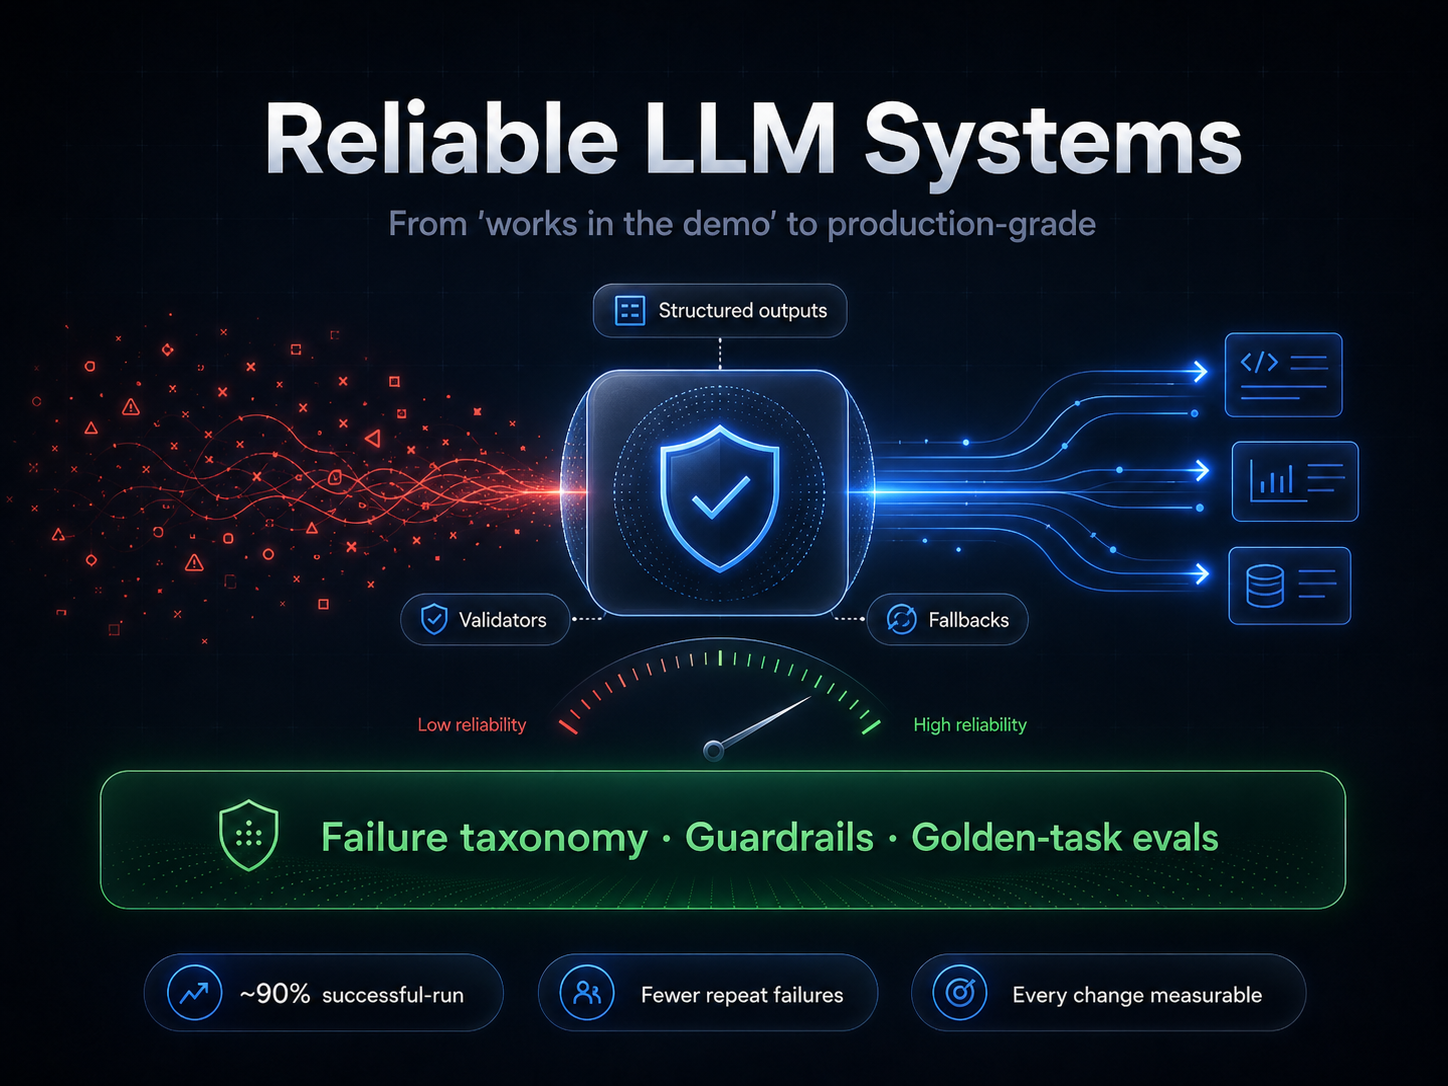
We add the reliability layer to flaky LLM features — structured outputs, validators, fallbacks and a failure taxonomy catching where multi-step reasoning breaks (loops, bad tool calls, context blowups) — and make every change measurable via evals.
We treat reliability as the product — not a finishing touch.
A demo proves the happy path. Production is the other 30%. We design for the failure modes first — that's where deployments actually live or die.
Evals before features. Every change is scored against your real data, so "better" is a number you can audit — not a vibe.
For government and enterprise, who-did-what and where-the-data-lives matter as much as accuracy. We build for the audit, not around it.
From a technical perspective they were great because of their analytical mindset — they approach every issue wanting to understand its root cause. Even more importantly, they have one of the best (and most underrated) skills: they are easy to work with, which matters even more in the stressful situations inevitable on any project.
I've directly managed hundreds of developers over my career, and this team is definitely among the top three. Incredible work ethic, a great attitude, and a pleasure to collaborate with when solving difficult problems… I'd highly recommend them for even the most complex builds and API integrations.
Engage us from whichever side of the world you're on. Same standards, same method, local contracting and time-zone coverage on both ends.
We'll tell you honestly whether we can help, and how we'd start — usually with the failure that's costing you the most, made measurable. Free 20-minute call, no pitch.